Vitalik Buterin Warns AI Could Break Lattice Cryptography Faster Than Expected
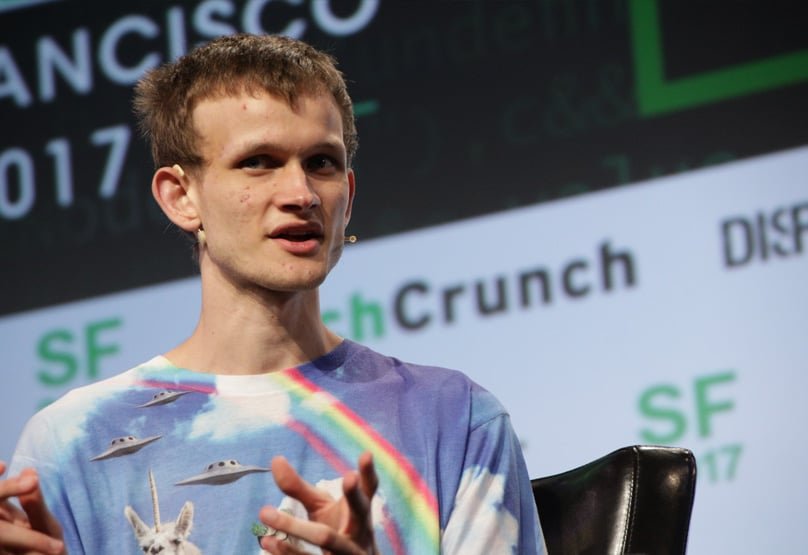
Vitalik Buterin has urged the crypto community to take AI-driven threats to cryptography seriously. The Ethereum co-founder said lattice-based schemes such as ML-DSA and FHE face growing risk from accelerated mathematical research.
He advised against rushing to move funds to new wallets. However, he recommended reducing exposure to both quantum-vulnerable and potentially AI-vulnerable cryptography. He also said ECDSA could fall sooner than many expect, which supports keeping funds in fresh addresses.
Why Lattice-Based Cryptography Faces New Scrutiny
Vitalik Buterin outlined the concern in a post on X. He said many people think elliptic curves are broken but hashes and lattices are safe. In his words, “there is a good chance that the concrete security of lattices will take serious hits.” He tied that risk to AI math over the next two years.
He compared the situation to factoring. Factoring naively takes 2^(n/2) time. Researchers later developed number field sieves and cut that to 2^O(n^(1/3)). Hence, RSA keys and signatures need about 400 bytes instead of 64 bytes.
Buterin then asked, “What if there are skeletons in the closet like that, both for elliptic curves and lattices?” He said humans may not be smart enough to discover them, “but bots soon will be.” He named ML-DSA, FHE, and lattices as the core new area of risk.
Buterin added a conditional scenario. If AI delivers 50 years of math in two years, lattices would need much larger parameters. At those sizes, hash-based constructions would beat lattice-based ones on efficiency wherever they apply.
Hash-Based Alternatives and Practical Recommendations
Ethereum’s lean roadmap has moved toward hash-only designs over the past year. It excludes lattices, ML-DSA, Falcon, and lattice-based commitments inside ZK proofs.
Signatures in lean Ethereum rely on hash-based schemes, either WOTS or SPHINCS-. Buterin said signatures and proofs can already go hash-only.
Public-key encryption presents a harder challenge. Vitalik Buterin said theorems show it cannot be built from hashes alone. It needs a trapdoor object with usable structure, such as lattices or code-based systems.
He expects AI to make some progress breaking that structure. His advice is to “multiply the key sizes by 10” for long-term security.
Buterin does not yet see a reason to pad the byte size of hashes. If concerns grow, he would increase round counts first. He noted that P = NP would break hashes but called it very unlikely. His summary was, “Hash-based > lattice-based, in those situations where hash-based is possible at all.”
The post also listed practical steps. Buterin advised keeping funds in addresses that have not made a transaction, if easy.
He warned, “I personally have lost more money in botched migrations than I have lost in all hacks combined.” Vitalik Buterin also favored offchain multisig confirmations and offchain delivery of encrypted privacy notes.
Originally published by blockonomi.com →